Building Security and Governance into Your AI Strategy
Build access controls, vendor assessment, human oversight and decision rights into AI strategy, with practical Australian privacy context for executives.
Todd Johnson
Founder, InnovateX Solutions
Published · 7 minute read
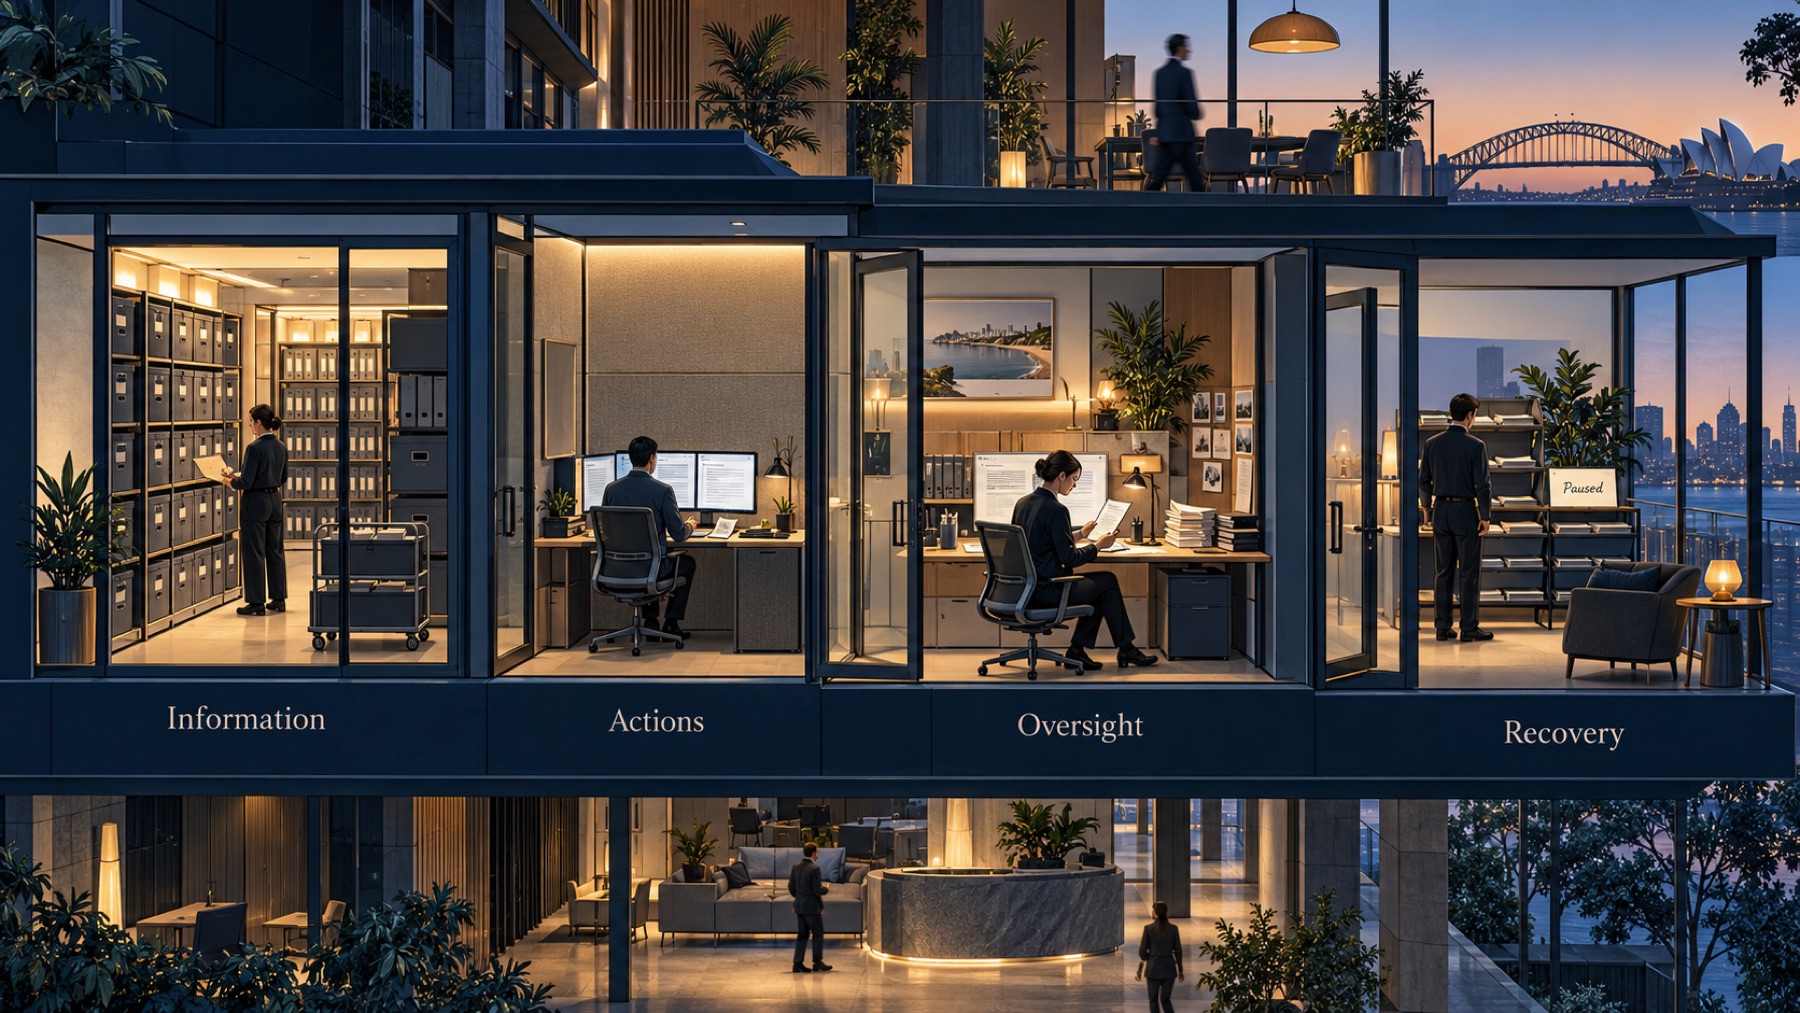
AI-created conceptual illustration.
An AI assistant that summarises an internal procedure and one that can change a customer’s account need different authority. Approving the software product doesn’t settle whether either use is appropriate.
For executives, security and governance need to answer questions about each proposed use. What information can it access? What is it allowed to do? Who is responsible for checking its behaviour, and who can intervene when something goes wrong?
Those decisions influence the strategy itself. They can change which opportunities you pursue, the supplier you choose and the cost of operating the result. An AI leader needs to understand those consequences well enough to discuss them alongside the expected business value.
Define the proposed use
Consider an illustrative customer service team introducing an assistant. In its first version, the tool searches approved product guidance and helps an employee draft a response. The employee checks and sends the reply through the existing system.
Later, someone proposes connecting customer records and allowing the assistant to issue credits. That change introduces access to additional information and authority to affect a customer account. The original approval should not be treated as permission for the expanded use.
Record the purpose and boundaries in language that business leaders and technical teams can both use. Identify the people affected, the information involved and the actions the system may take. Specify the situations that need a person and the changes that trigger a fresh review.
Keep that record with an accountable business owner. It can sit within existing risk and change processes if they can handle the decisions. A separate committee isn’t required for every small use, but a small use still needs someone who understands its scope.
Know which Australian requirements apply
For organisations covered by the Privacy Act, existing obligations apply when AI handles personal information. Coverage depends on the entity and circumstances. The OAIC explains that organisations with annual turnover above $3 million generally have responsibilities, subject to exceptions, and that some smaller organisations are also covered. A turnover threshold alone is not a complete assessment. OAIC rights and responsibilities.
The OAIC’s AI guidance addresses personal information in both inputs and outputs. It also warns that inferred or inaccurate information about an identifiable person can still be personal information. Executives should therefore ask what a system creates about people as well as what employees upload. As a matter of best practice, the OAIC recommends against entering personal information, particularly sensitive information, into publicly available generative AI tools. OAIC guidance on commercially available AI products.
A paid enterprise product still needs assessment for the intended use. Involve your privacy and legal advisers in examining the purpose for handling the information and the obligations that follow from the actual data flow. Supplier marketing is not that assessment.
Check the arrangements for overseas handling. APP 8 can apply to disclosure of personal information to an overseas recipient. The OAIC distinguishes disclosure from circumstances in which an entity retains effective control and the handling may be a use. Assess both the contractual arrangements and who can access the information. OAIC APP 8 guidance.
There is also an approaching transparency requirement. From 10 December 2026, APP entities must include specified information in their privacy policies where they have arranged for a computer program to use personal information to make a decision, or do something substantially and directly related to making it, and the decision could reasonably be expected to significantly affect an individual’s rights or interests. The disclosure covers the kinds of personal information and decisions involved. A person participating in the process does not automatically put it outside the requirement. OAIC update published 30 September 2026.
As at 12 October 2026, that commencement date is still ahead. Review relevant processes now with the people responsible for privacy compliance. Examine processes such as recruitment screening and customer eligibility against the legal conditions. Do not assume every AI use is covered or that only fully automated decisions qualify.
This is a general executive overview. The requirements for an actual use depend on your organisation, sector and circumstances, including any other applicable laws and contractual duties.
Examine the supplier and the whole data path
Ask procurement and technical teams to follow the information through the proposed service. The assessment should cover what is submitted, where it is processed and retained, and who else may access it. Include connected services, support arrangements and any subcontractors relevant to the data flow.
Establish whether information may be used for model training and how the applicable settings and terms are enforced. Check retention and deletion arrangements, including what happens when your organisation leaves. Establish how changes to the service or terms will be communicated and assessed.
Your business may require Australian hosting. It doesn’t by itself answer who has access, where support is performed or what connected services do. Examine those questions directly.
The Australian Signals Directorate’s Australian Cyber Security Centre advises organisations to understand how AI services handle their data and to assess the security implications of using them. Its guidance also addresses AI specific threats such as malicious inputs intended to manipulate system behaviour. ASD’s ACSC guidance on engaging with AI.
Ask the implementation team to test an untrusted document containing instructions that conflict with the assistant’s approved task. Check whether the assistant treats those instructions as document content or follows them. If it has permission to take actions, test the limits of that authority in a safe environment too.
Make access and oversight work in practice
The customer service assistant should only retrieve information appropriate to the employee and the approved purpose. Test the boundary using accounts with different permissions. Confirm what happens when access is removed and when a document becomes restricted.
Treat reading and acting as separate permissions. An assistant may be allowed to prepare a suggested credit explanation without being allowed to issue the credit. If the business later authorises account changes, it needs defined limits, checks and a record of what happened.
Allocate time for human review and give reviewers access to the evidence behind the output. A reviewer should be able to inspect the relevant source, recognise when the answer is uncertain and reject the recommendation. If staff are expected to approve a large queue rapidly without seeing supporting information, the review step may provide little protection.
Choose the checks according to the consequence of an error. A wrong internal summary and an incorrect decision affecting a person warrant different responses. Test representative cases before release, including missing information, conflicting records and attempts to exceed the approved scope.
Keep governance active after release
Once the system is operating, assign responsibility for reviewing incidents, complaints and changes in performance. Decide who can pause it and how the team will continue the process without it. Run through that response before it is needed.
Keep records of approvals and system behaviour without collecting more sensitive material than necessary. Decisions, permissions and test results can help explain why a use was approved. Logs need their own access and retention rules because they can contain information as sensitive as the original records.
Australia’s National AI Centre provides adoption guidance on accountability, risk and ongoing oversight. It is government guidance, not a substitute for determining the legal obligations of a particular use. National AI Centre implementation guidance.
For your next AI proposal, ask the accountable leader to show how the controls affect the implementation and the business case. If a necessary check adds substantial operating effort, that effort belongs in the cost estimate. If a restriction makes the proposed use unsuitable, the strategy needs to change before the investment proceeds.
Questions
Is Australian hosting enough to make an AI service suitable?
Does human review make an AI process safe?
What should trigger a fresh approval?
Written by Todd Johnson
Founder of InnovateX Solutions. Todd provides fractional CIO, CTO and Chief AI Officer leadership for Australian businesses and government, and wrote the XAF Connected Architecture framework.
Todd on LinkedIn